
Built for trust. Designed for privacy.
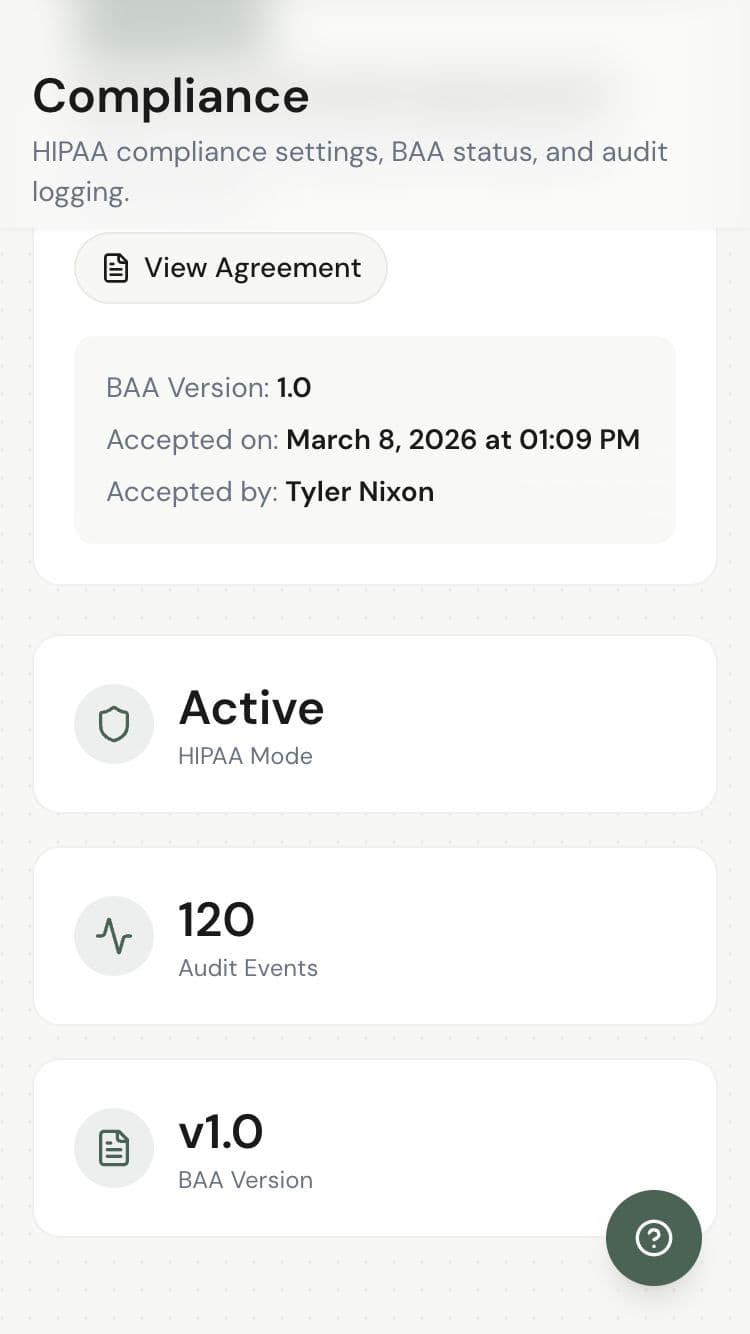
US practices accept a Business Associate Agreement right in the app. Clinical notes are encrypted, data runs on HIPAA-eligible AWS infrastructure, and a PHI audit log shows activity on client records.
Security you can see.
Your compliance page shows your BAA status, the PHI audit log, and how your data is protected. Owners and admins accept the BAA there, and anyone on the team can turn on two-factor sign-in or a passkey.
Clinical data,
always protected.
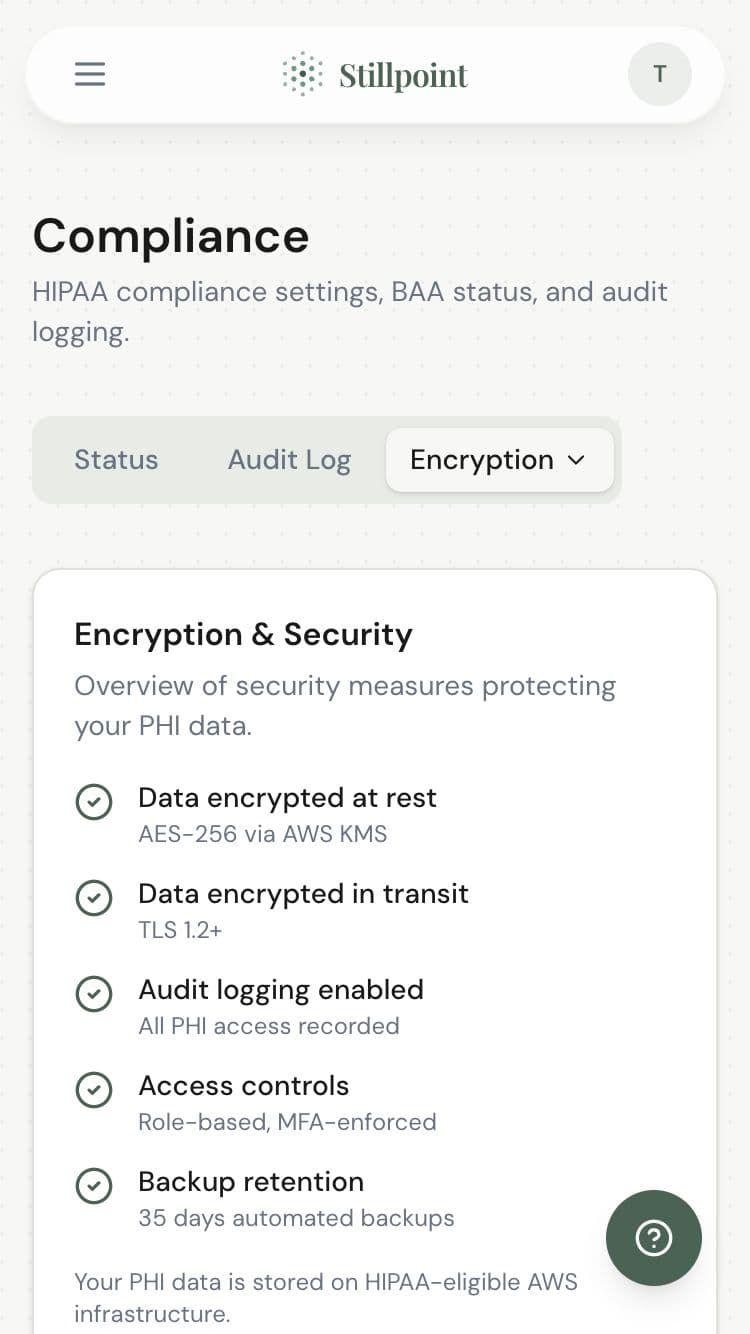
Everything is encrypted at rest with AES-256 and in transit with TLS 1.2 or later. SOAP notes get a second layer of encryption in the app, and role-based access keeps clinical records away from front desk staff.
Encrypted at rest
AES-256 at rest through AWS KMS. SOAP notes are also encrypted in the app with AES-256-GCM before they are stored.
Role-based permissions
Four roles: owner, admin, practitioner, and scheduler. Schedulers can't open clinical records.
Sign-in protection
Optional two-factor authentication and passkeys, and sessions lock after 15 minutes idle.
A record of
who did what.
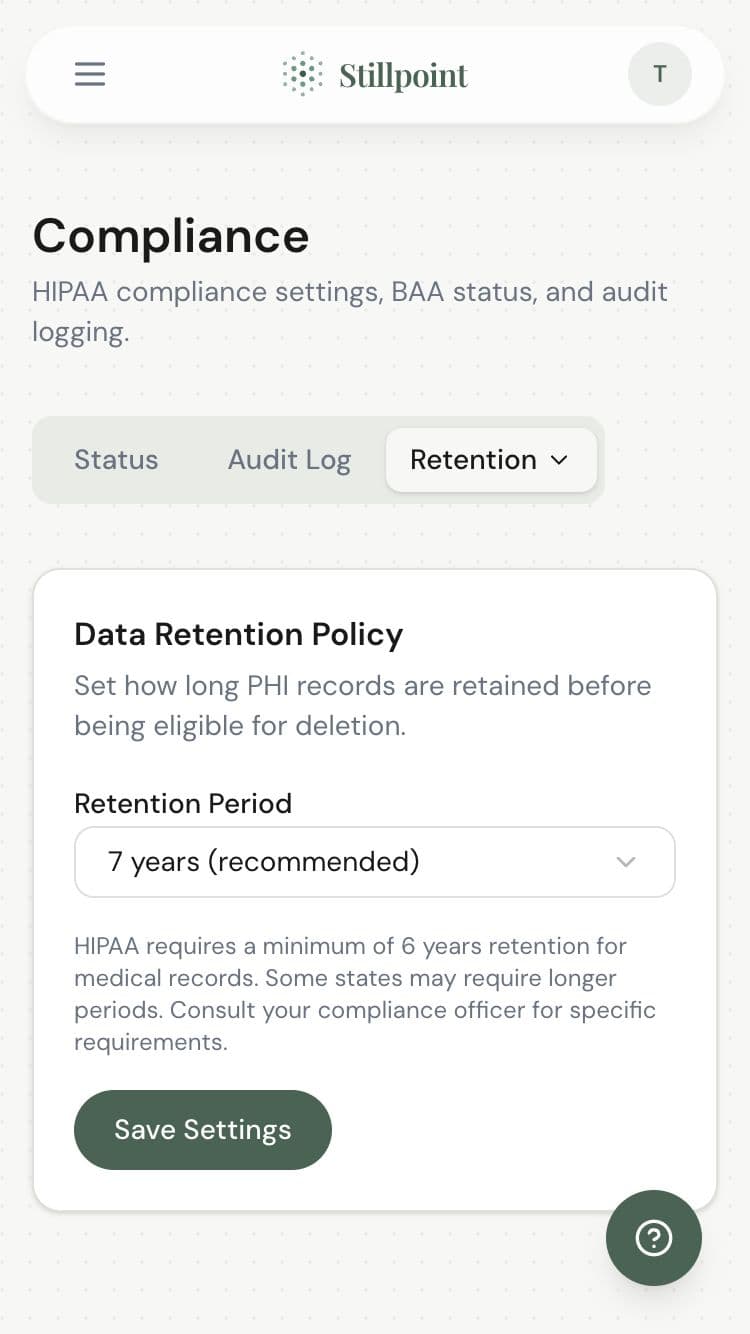
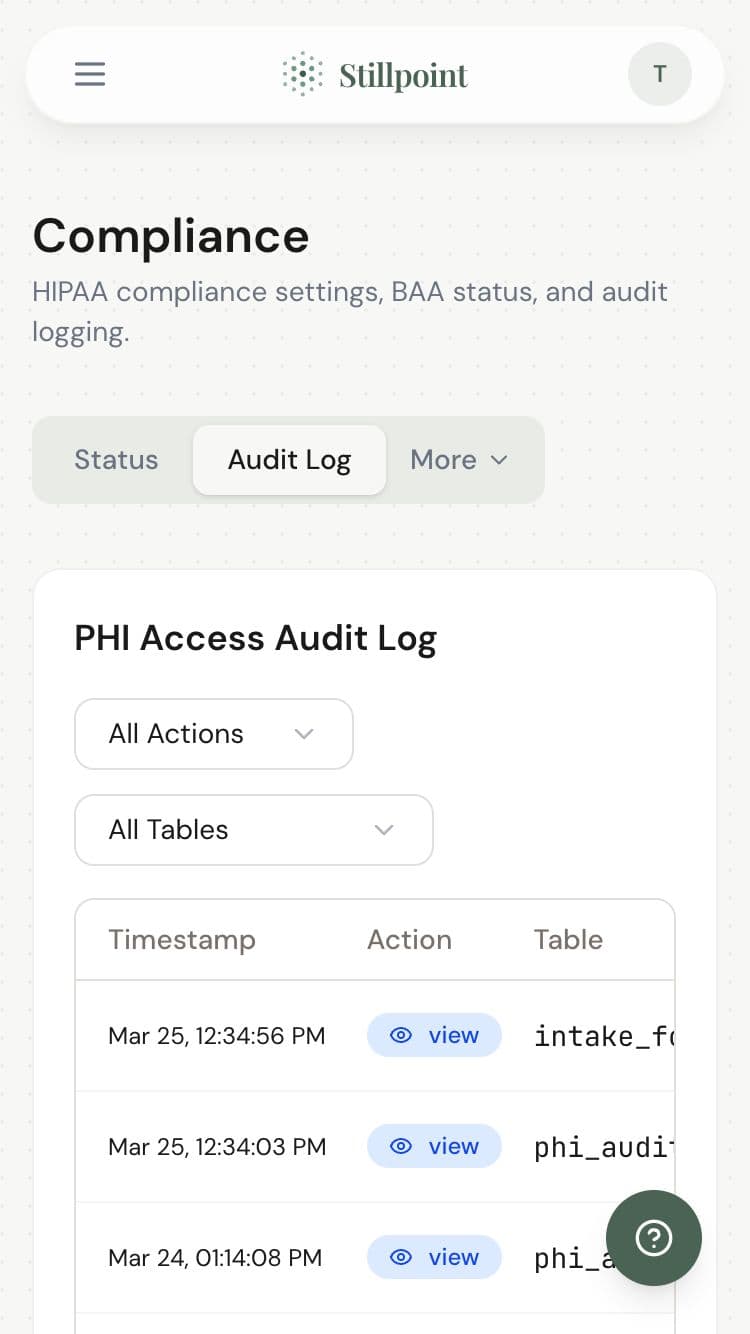
A PHI audit log records activity such as viewing, editing, and exporting clinical notes and intake forms. Your accepted BAA is always one click away, and automated backups are kept for 35 days.
PHI access audit log
Filter by action, record type, and date to see who opened or changed a record, and when.
Accepted BAA on file
Owners and admins accept the BAA in the app. It is versioned with its acceptance date, and you can view it or download a PDF any time.
35-day backups
Automated database backups are kept for 35 days, with point-in-time recovery.
Ready when you are.
Join wellness practitioners who use Stillpoint to fill their schedule and focus on what matters most.
Start Free© 2026 Stillpoint